
Security First
Every decision we make prioritizes the security and privacy of our customers and their users.
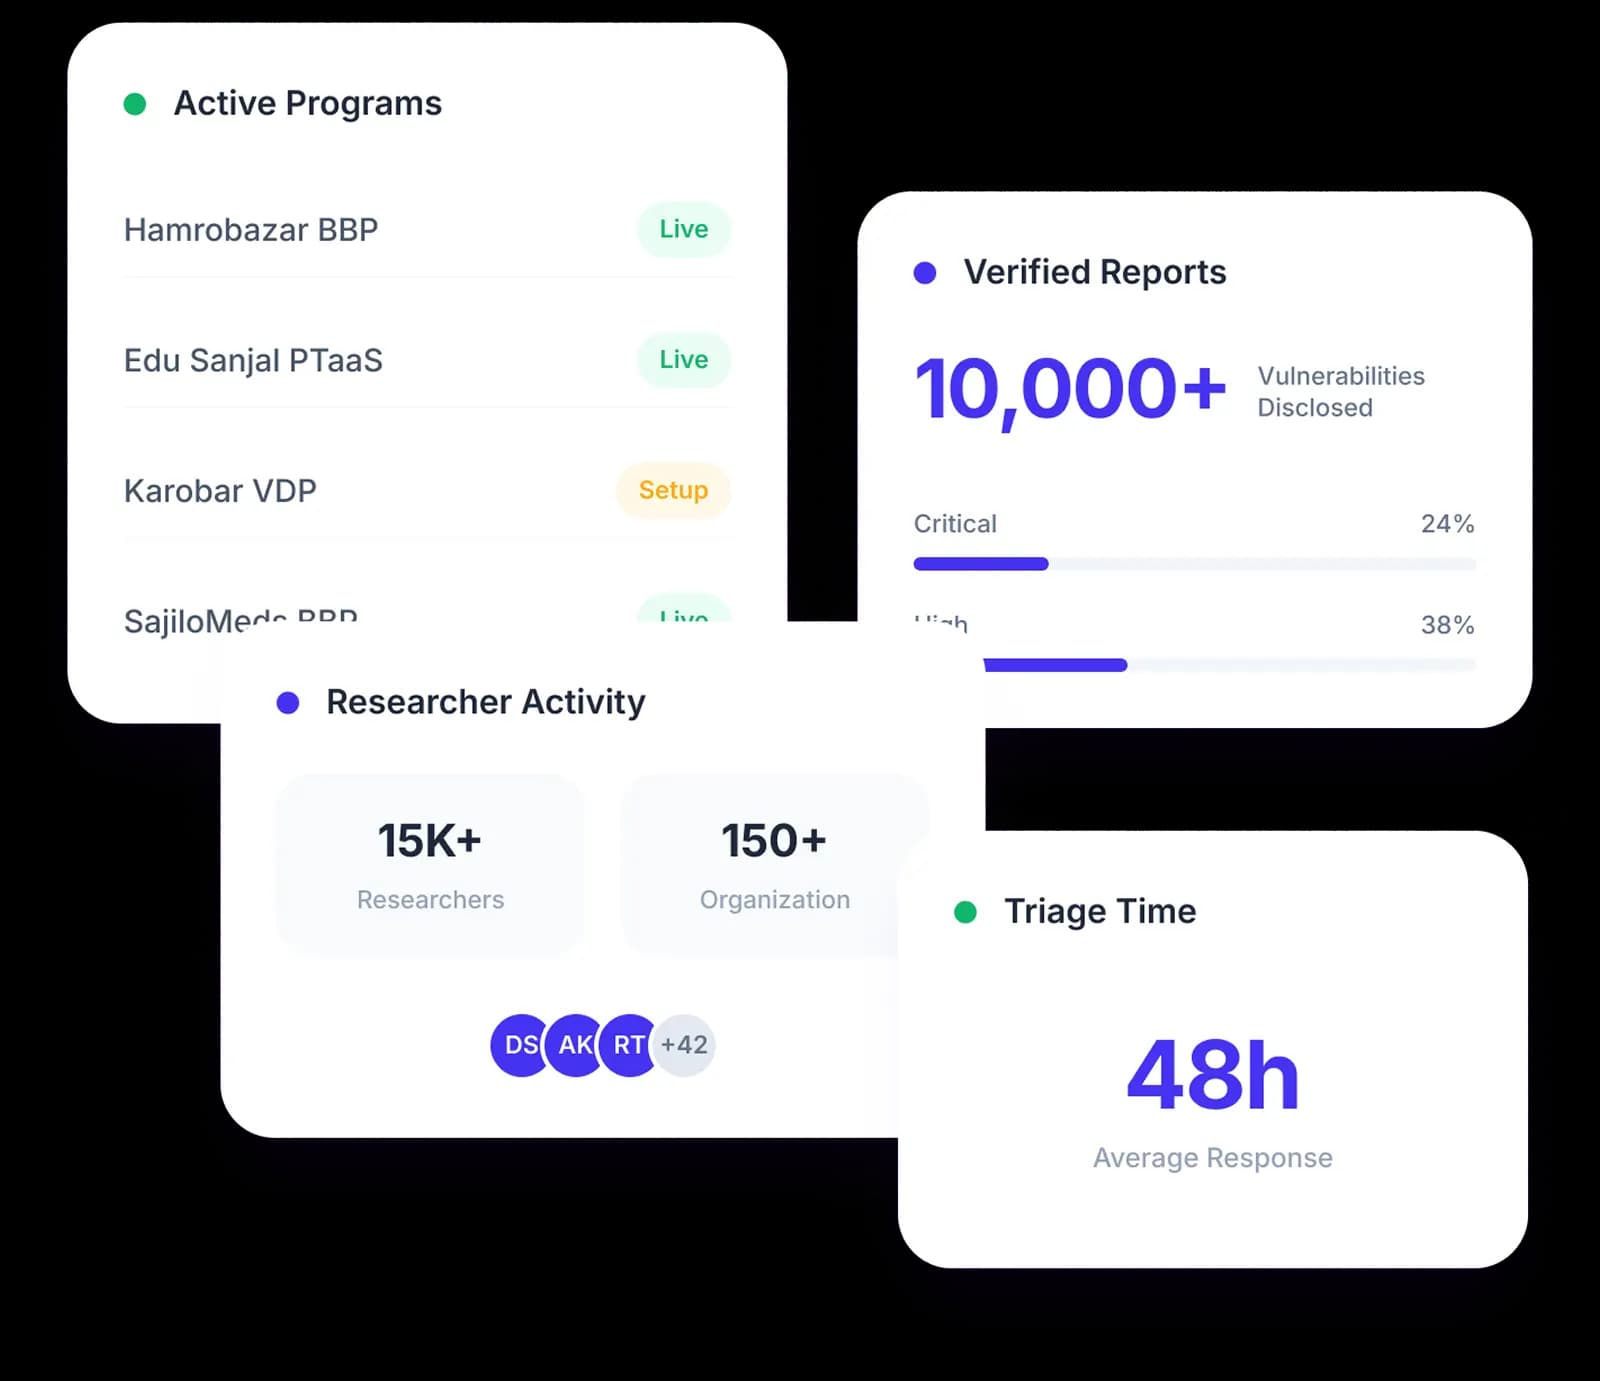
Our mission is to connect organizations with security researchers through transparent, responsible vulnerability disclosure—making it easier to identify, resolve, and prevent security risks before they become threats.
Every decision we make prioritizes the security and privacy of our customers and their users.
Security is not a destination. We help organizations build resilient, adaptive security programs.
We partner with security researchers worldwide to surface critical vulnerabilities before exploitation.
 Our Story
Bugv began with a simple observation: the way most organizations tested for vulnerabilities looked nothing like the way they shipped software.
Security testing was episodic, annual pentests couldn't keep pace with weekly releases.
Security testing was episodic, annual pentests couldn't keep pace with weekly releases.
Traditional engagements delivered PDF reports weeks after issues were introduced.
Traditional engagements delivered PDF reports weeks after issues were introduced.
Findings lived in email threads. Ownership, priority, and status were unclear.
Findings lived in email threads. Ownership, priority, and status were unclear.
The world's best researchers lacked a trusted, structured way to work with enterprises.
The world's best researchers lacked a trusted, structured way to work with enterprises.
One platform for Bug Bounty, PTaaS, and VDP with verified triage and clean workflows.
One platform for Bug Bounty, PTaaS, and VDP with verified triage and clean workflows.
Findings flow from researcher to engineer with context, in hours instead of months.
Findings flow from researcher to engineer with context, in hours instead of months.
Our ValuesEvery decision is weighed against the risk it introduces for us and for our customers.
Status, scope, and payout terms are visible to everyone involved, no black boxes.
Coordinated, ethical, and structured, protecting users first.
Every workflow, contract and payout is designed to earn it.
We measure ourselves by remediation, not report volume.
Shipping small, meaningful improvements every week.
Run bug bounty, PTaaS, and VDP programs on one platform built for teams who take security seriously.
