Instant Audit Deliverables
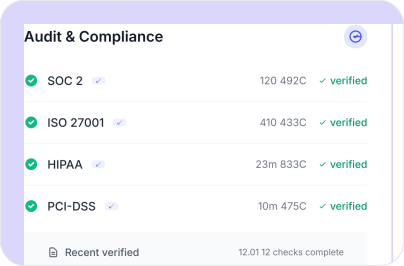
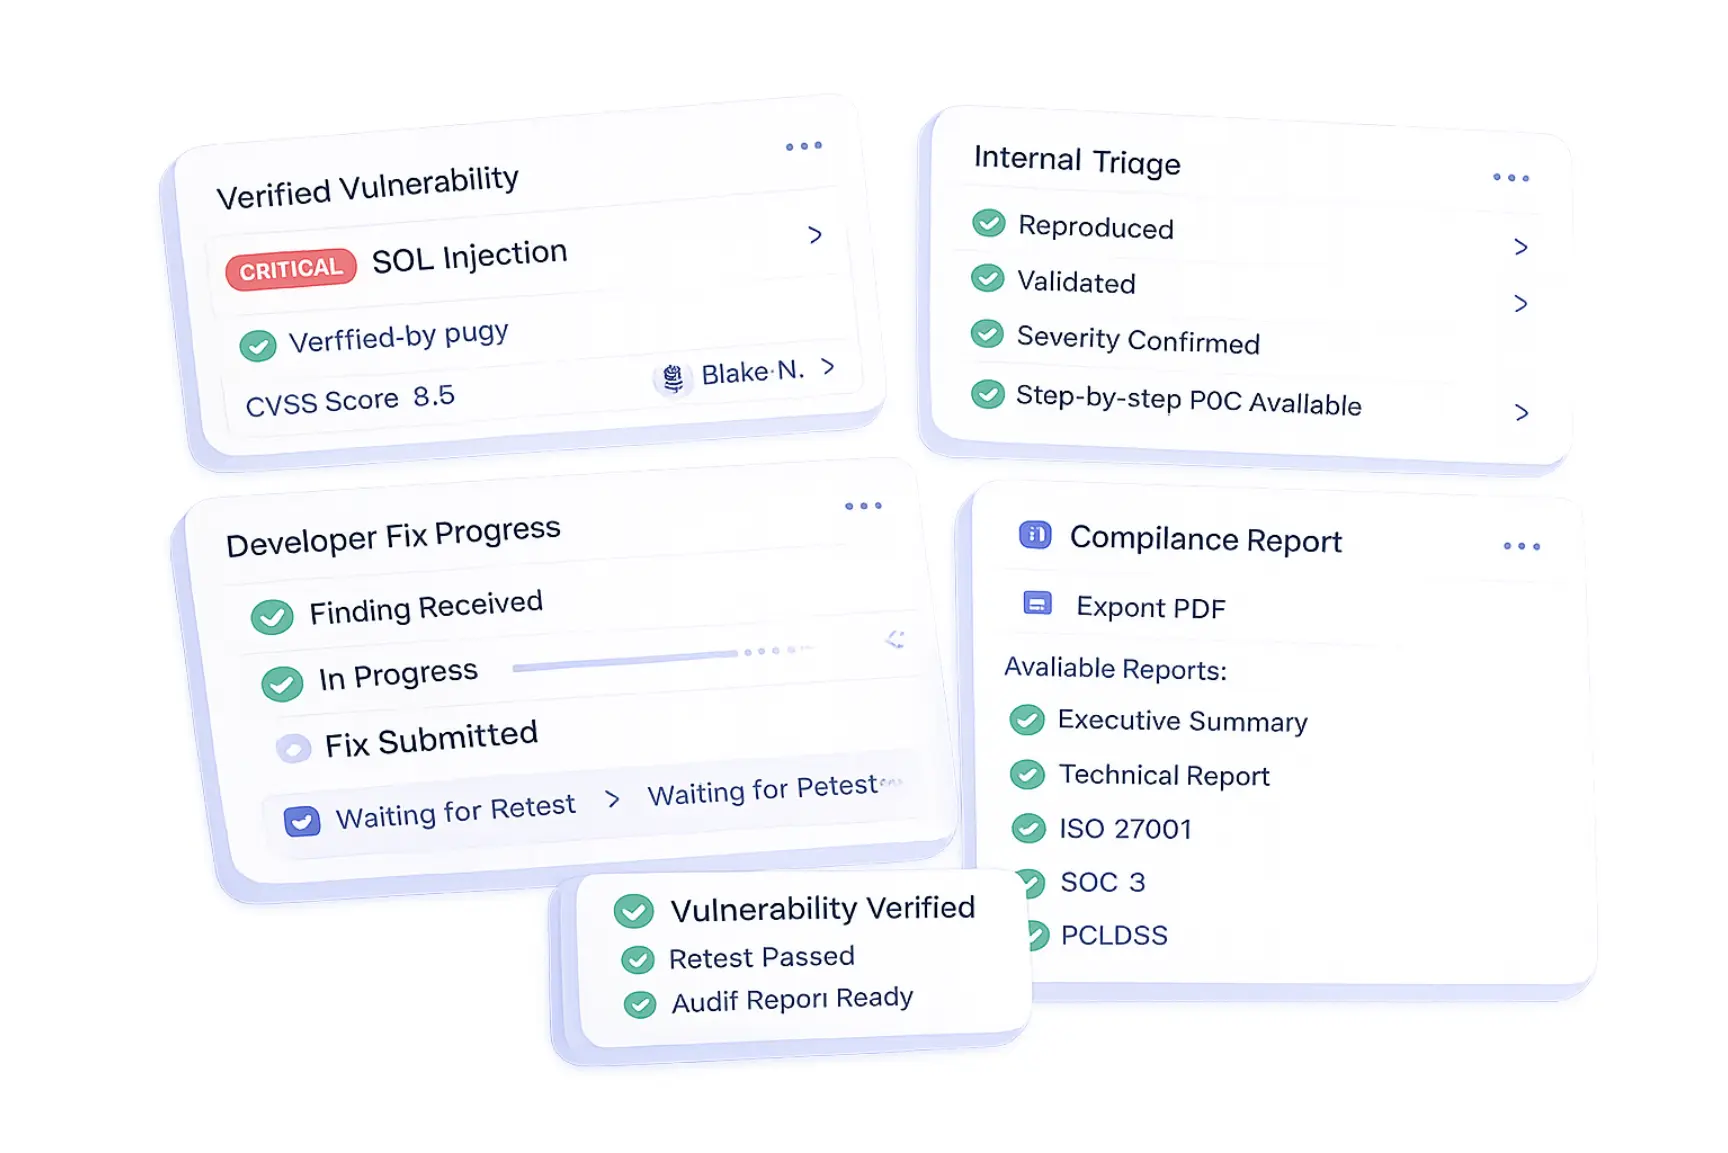
Generate official, presentation-ready compliance reports with a single click. Formatted specifically to satisfy auditors for SOC 2 Type II, ISO 27001, PCI-DSS, and vendor security assessments.
Predictable, human-led penetration testing built for compliance and fast remediation.
Generate official, presentation-ready compliance reports with a single click. Formatted specifically to satisfy auditors for SOC 2 Type II, ISO 27001, PCI-DSS, and vendor security assessments.
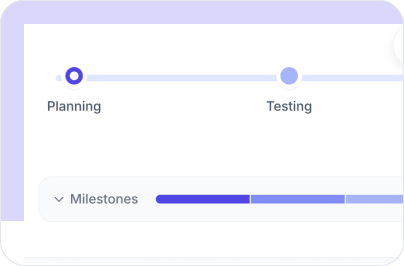
No unexpected bounty costs or open-ended spending. Get strict, upfront scoping with guaranteed deliverable dates.
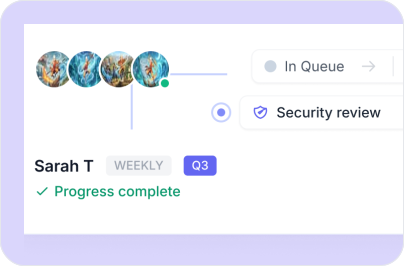
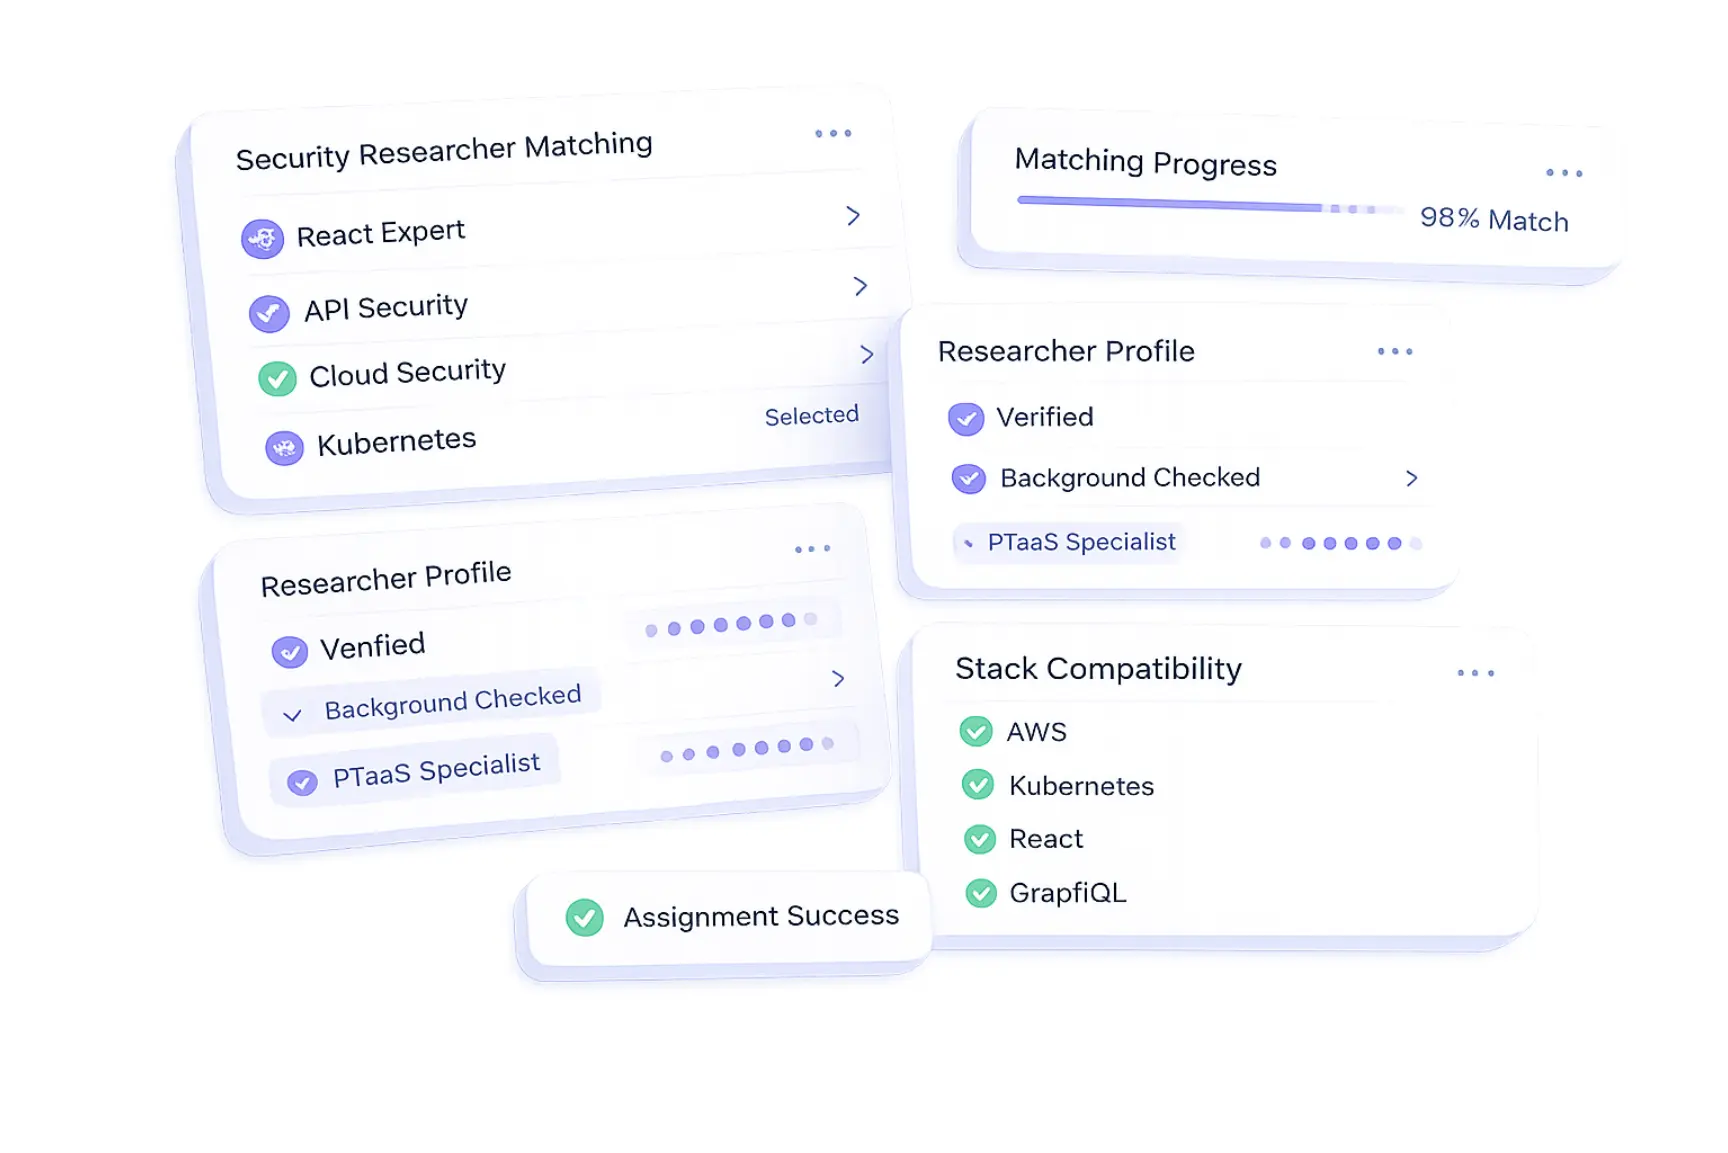
Instead of an open crowdsourced model, your assets are assigned to dedicated, background-checked specialists specific to your tech stack.
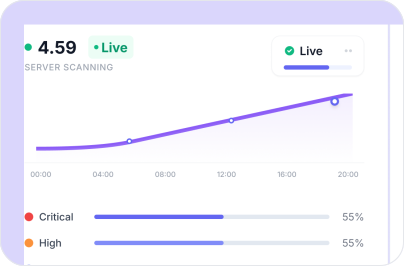
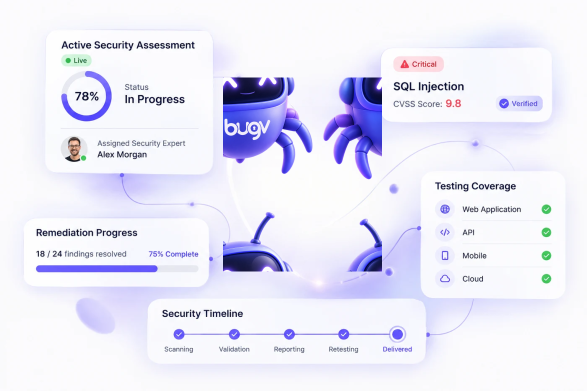
Track engagement progress as it happens. Monitor testing completion percentages, active target assets, and severity breakdowns directly from your centralized dashboard.
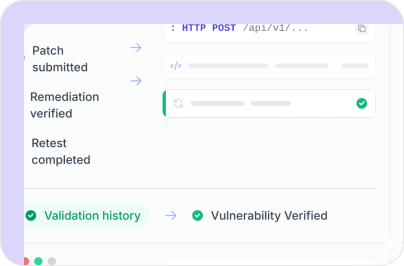
Once your engineering team patches a vulnerability, trigger a retest request straight from the dashboard to verify the fix without paying extra consulting fees.
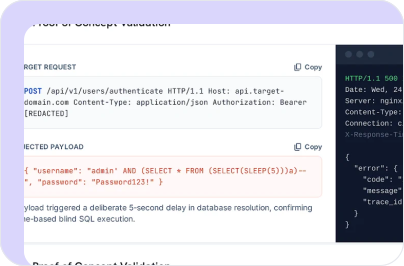
Every finding includes clear reproduction steps, video or screenshot proof, and tailored code-level guidance to help developers fix issues fast.
Test web applications, APIs, mobile apps, networks and other approved attack surfaces through one security testing workflow.
 Workflow
Move from vulnerability discovery to patching in one connected workflow. Review findings, prioritize risk and keep your team focused on fixing what matters.
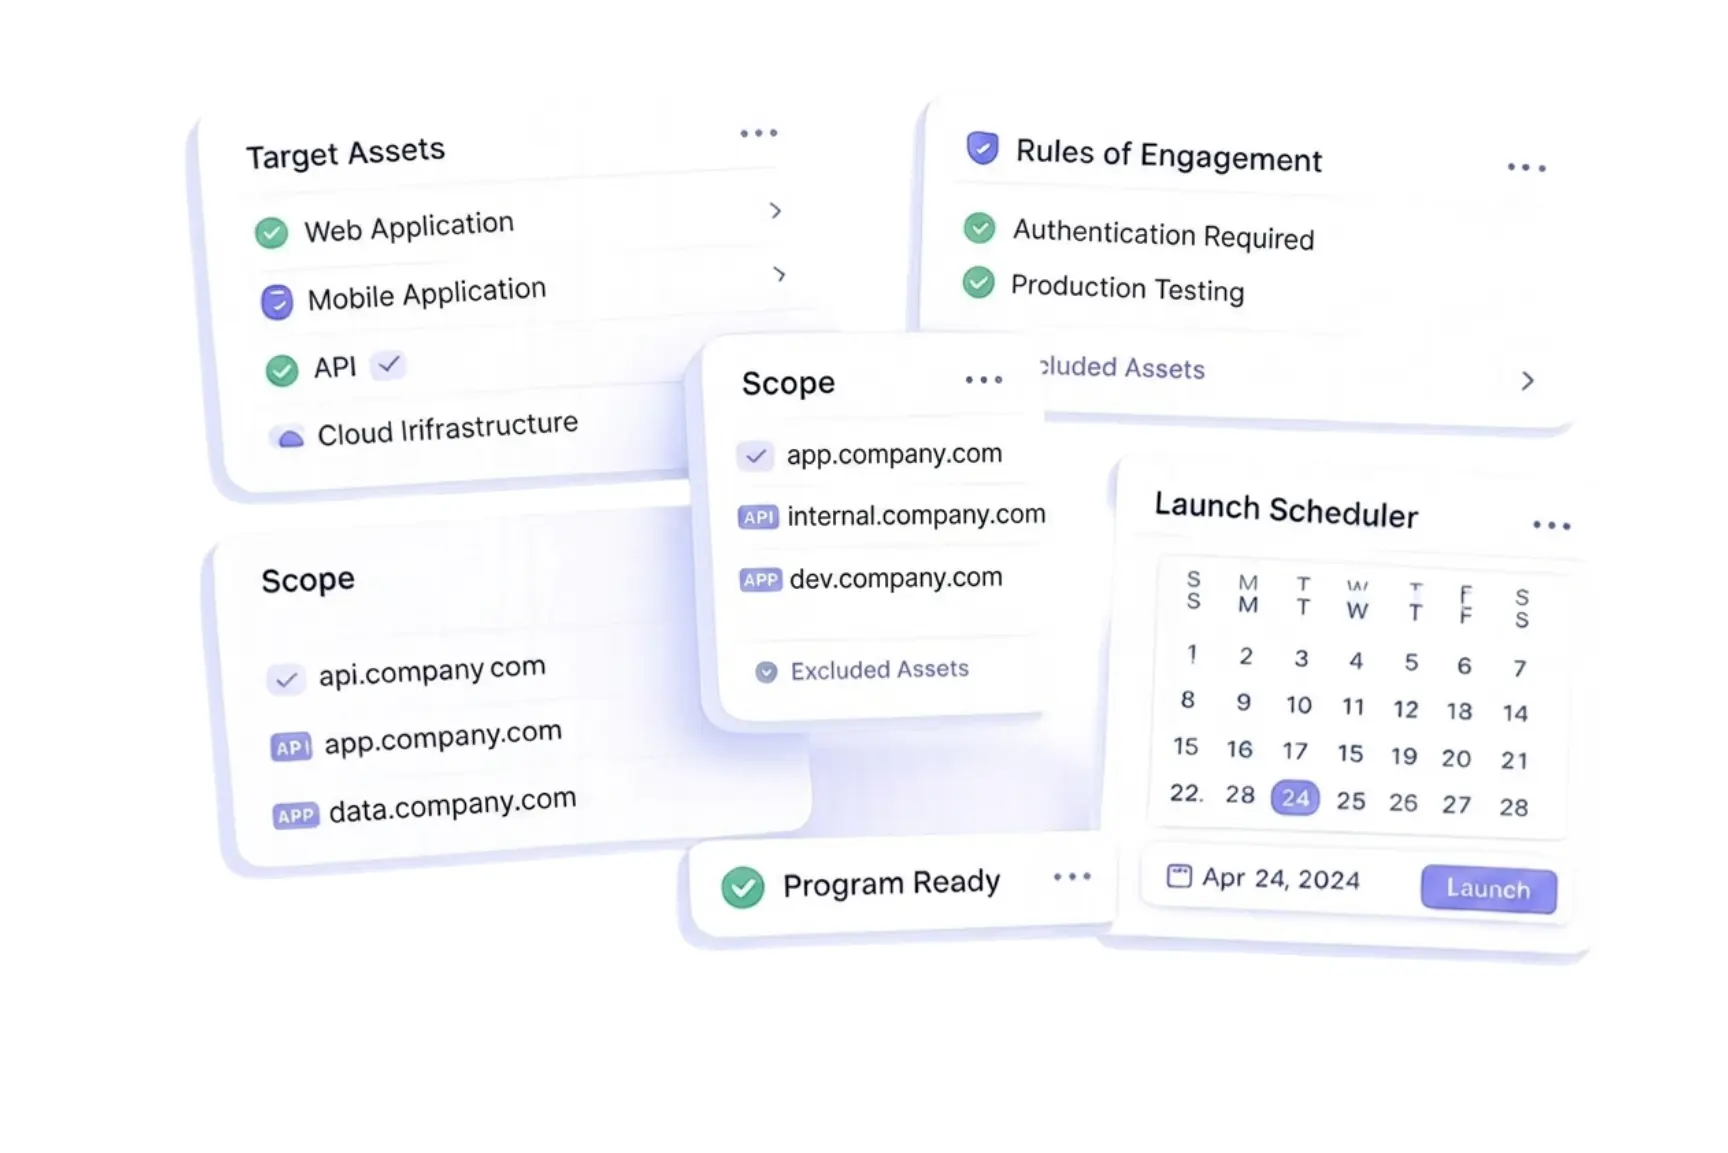
STEP 01
Configure your targets, define the Rules of Engagement, and launch your assessment in minutes.
STEP 02
STEP 03
See how Bugv helps your team launch, manage and measure a security program.
Bugv delivers measurable financial impact compared to traditional security approaches.