Human Expertise at Scale
Find real security issues with skilled researchers testing your applications from different angles.
Traditional security testing captures a moment in time. Bug bounty programs help teams continuously discover and fix vulnerabilities as they emerge.
Find real security issues with skilled researchers testing your applications from different angles.
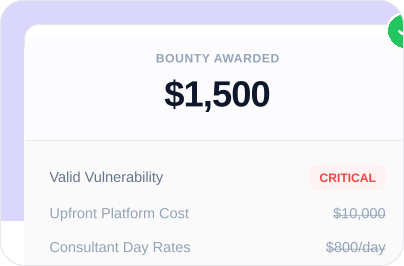
Pay only for valid vulnerabilities instead of costly time-based security testing.
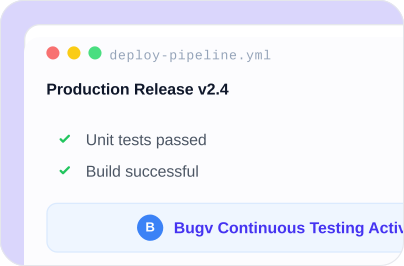
Keep your applications under continuous testing as new code and vulnerabilities emerge.
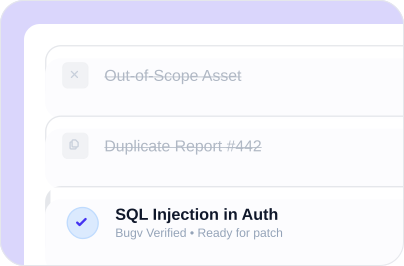
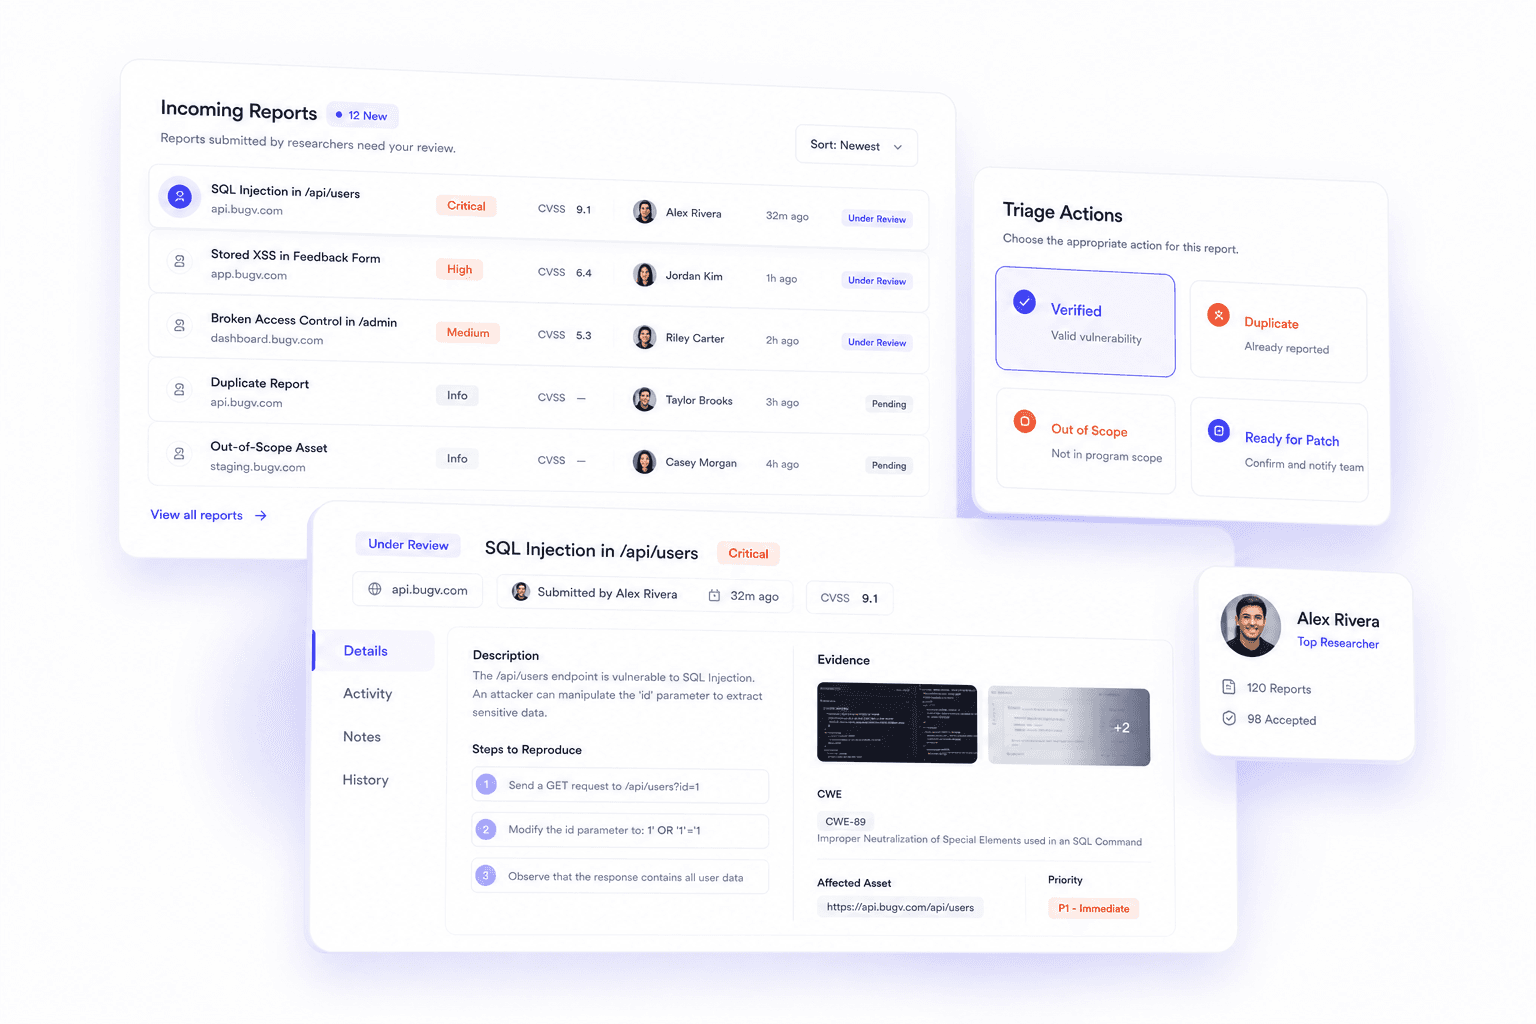
Get verified reports without duplicate, out-of-scope, or low-quality submissions.
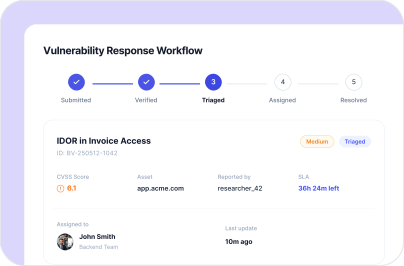
Validate security findings faster with researchers who reproduce issues and provide clear evidence.
Find complex vulnerabilities through researchers with different skills, methods, and security expertise.
Choose between open and private programs with full control over who can participate.
Open access. Maximum researcher each
Open your program to a broad community of security researchers and maximize testing coverage across your attack surface.
Invite-only. Maximum control.
Work with selected researchers through a controlled program designed around your security needs.
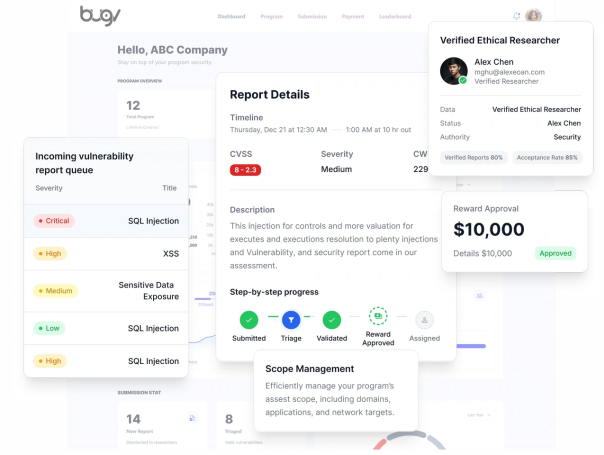
Manage every stage of your bug bounty program—from program setup and researcher collaboration to verified reports, reward management, and actionable insights—all within a single platform.
Define and manage your attack surface with surgical precision. Keep your assets perfectly mapped and monitored.
Access a vetted pool of 15,000+ global security experts. Connect with top talent tailored to your specific stack.
Seamless, automated payouts for verified vulnerabilities. Handle global compliance and tax forms effortlessly.
Gain immediate insights into your security posture and program performance with dashboards.
 Workflow
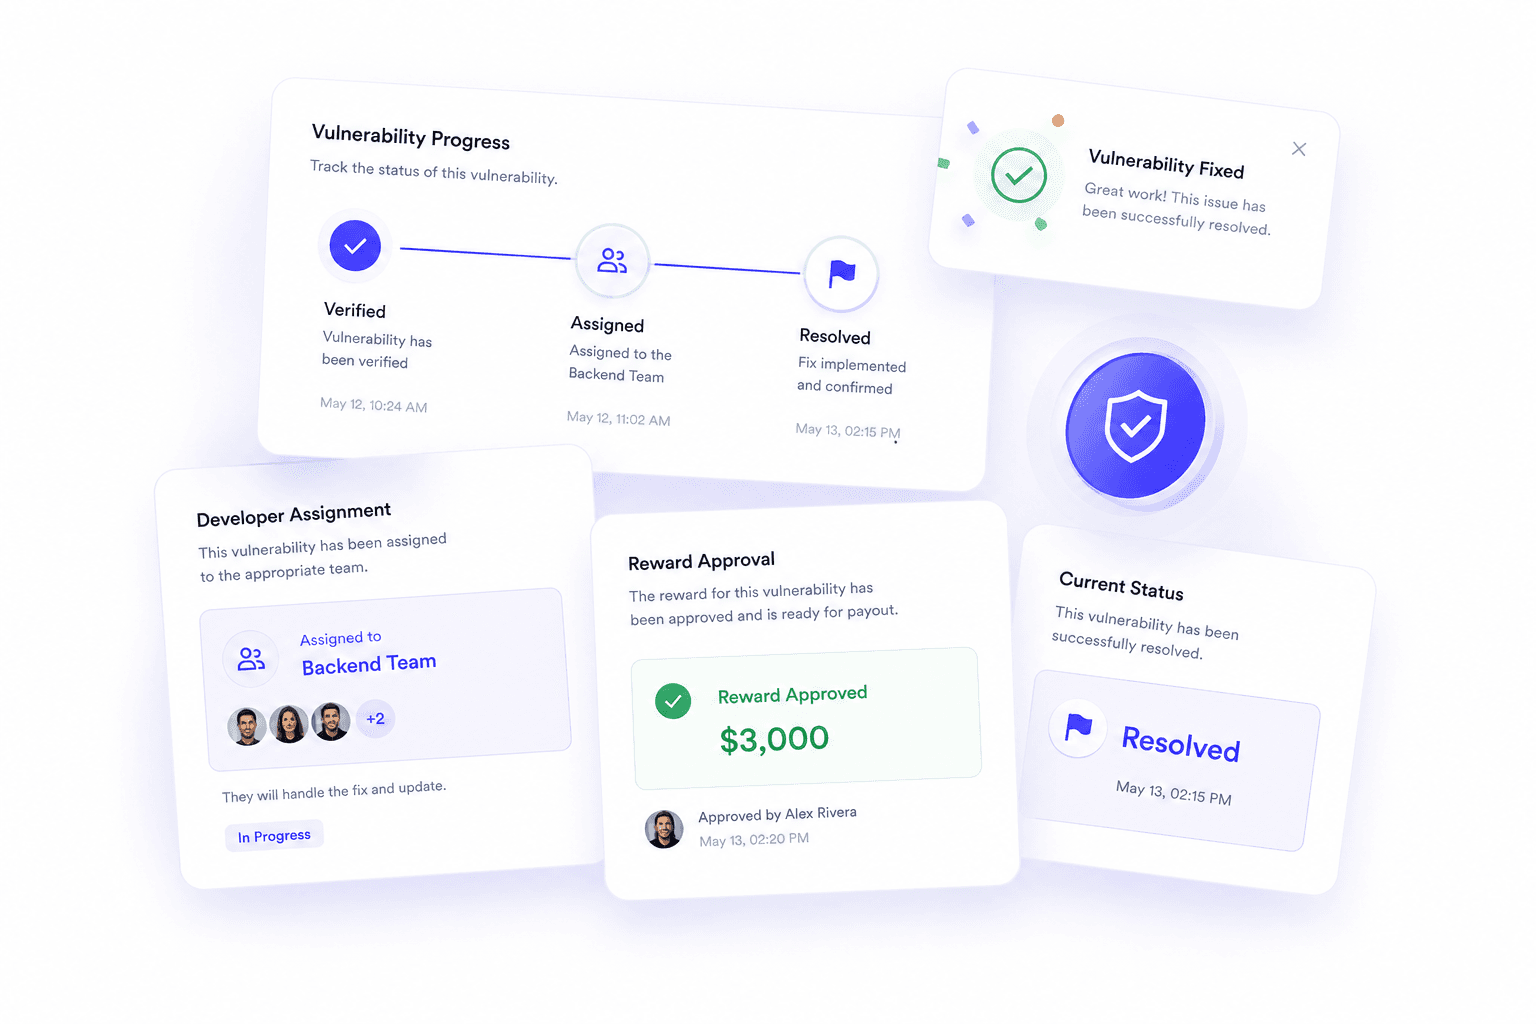
Move from vulnerability discovery to patching in one connected workflow. Review findings, prioritize risk and keep your team focused on fixing what matters.
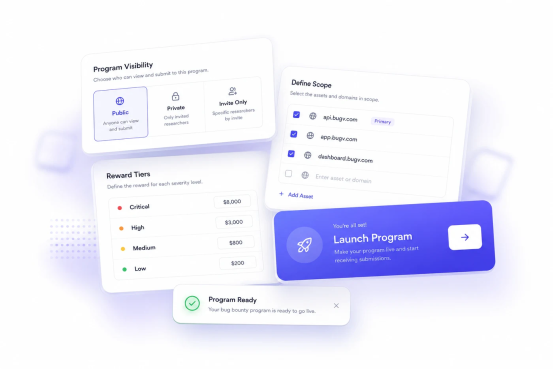
STEP 01
Create a public or private bug bounty program by defining scope, reward tiers, policies, and eligible assets.
STEP 02
STEP 03
Extend your security coverage without adding every testing capability in-house.
AVERAGE BREACH COST (IBM 2024)
Up to 73% lower breach impact$4.88M
The average cost of a data breach continues to rise. Proactive bug bounty programs reduce incident likelihood by up to 73%.
COST COMPARISON
Pay only for validated vulnerabilitiesTIME TO FIX
18x faster remediationReal-Time Validation
Verified reports reach your engineering team sooner through continuous security testing and expert triage.
SECURITY APROACH
Traditional penetration testing happens 1-2 times per year. Bugv programs run 365 days a year, providing ongoing protection.
See how Bugv helps your team launch, manage and measure a security program.
Bugv delivers measurable financial impact compared to traditional security approaches.
Launch a bug bounty program, engage trusted security researchers, and resolve verified vulnerabilities from one centralized platform.
Personalized platform walkthrough
No commitment required
30-minute live demo
Built for modern security teams